On September 24, 2026, Bloomberg reported that the fallout resulting from the recent inadvertent disclosure of an internal deal pipeline by a senior investment banker at Morgan Stanley highlights one of the most persistent operational vulnerabilities in financial services: the human element in sensitive communications. When confidential deal lists covering prospective initial public offerings (IPOs), private equity sponsor deals, and blocked trades leak into the public domain, financial institutions face potential regulatory scrutiny and exposure to civil litigation. Moreover, each regulator “expects intermediaries to have robust internal controls in place to protect their clients’ confidential information and prevent data leakage, which may harm the interests of their clients or impact the integrity of the market.”
Wall Street litigators will be evaluating client claims, defense positions, or regulatory enforcement actions arising from inadvertent disclosures and considering whether a firm breached its industry standard of care, which requires a structured, evidence-based liability analysis. This article outlines the publicly known facts of the Morgan Stanley incident and details the analytical steps a compliance expert witness would likely undertake to evaluate liability in litigation resulting from the deal leakage.
Factual Context & Regulatory Exposure
Understanding the precise mechanics and post-incident response is fundamental to any expert evaluation:
- Incident Mechanics: According to Bloomberg, Mohamed Atmani, the Asia-Pacific head of financial sponsors in Morgan Stanley’s investment banking department, intended to distribute a client-facing private equity market update. Instead, an email was sent inadvertently attaching an internal pipeline listing more than 100 confidential deals across Asia, Europe, the Middle East, and Africa. The list detailed IPO candidates across China, South Korea, and India, private equity and pension fund backers, and stalled projects.
- Immediate Containment: The banker sought to recall the email, and the firm immediately engaged key clients and financial sponsor executives through personal outreach and apologies. Morgan Stanley issued internal directives requiring staff to escalate any client or media inquiries to senior management and instructed employees to complete compliance training on handling misdirected emails. The firm stated publicly that it took prompt steps to address the inadvertent sharing and continues to prioritize client confidentiality.
- Market & Regulatory Reactions: Competitors circulated the list, with some bankers indicating intent to target listed transactions, while peer institutions like Goldman Sachs issued internal memos instructing staff not to store or distribute the document on personal or company devices. Regulators across jurisdictions responded: Hong Kong’s Securities and Futures Commission (SFC) noted its expectation that intermediaries maintain robust internal controls to prevent data leakage, while China’s CSRC and India’s SEBI initiated assessments.
- Early Impact Assessment: While Morgan Stanley reported no client disengagement following the leak, disclosures regarding upcoming block trades or share placements create inherent market risks, including downward price pressure on underlying equities prior to execution.
Step-by-Step Compliance Liability Analysis Framework
When retained by litigators in cases involving leaked transaction pipelines or misdirected sensitive data, a compliance expert follows a multi-stage liability framework to assess the standard of care and breach response:
Establishing the Standard of Care and Contractual Duties
The expert begins by mapping the firm’s legal and regulatory obligations regarding material non-public information (MNPI):
- Contractual Commitments: Reviewing non-disclosure agreements (NDAs) and engagement letters governing the transactions on the leaked pipeline to determine explicit confidentiality covenants and notice requirements.
- Regulatory Benchmarks: Measuring firm policies against global regulatory expectations, such as HK SFC guidelines requiring robust internal controls to prevent data leakage, or FINRA/SEC rules governing supervisory systems (e.g., FINRA Rule 3110) and sensitive customer information protection.
Evaluating Technical and Administrative Control Design
A core duty of the expert is to evaluate whether the institution maintained reasonable preventive controls prior to the event:
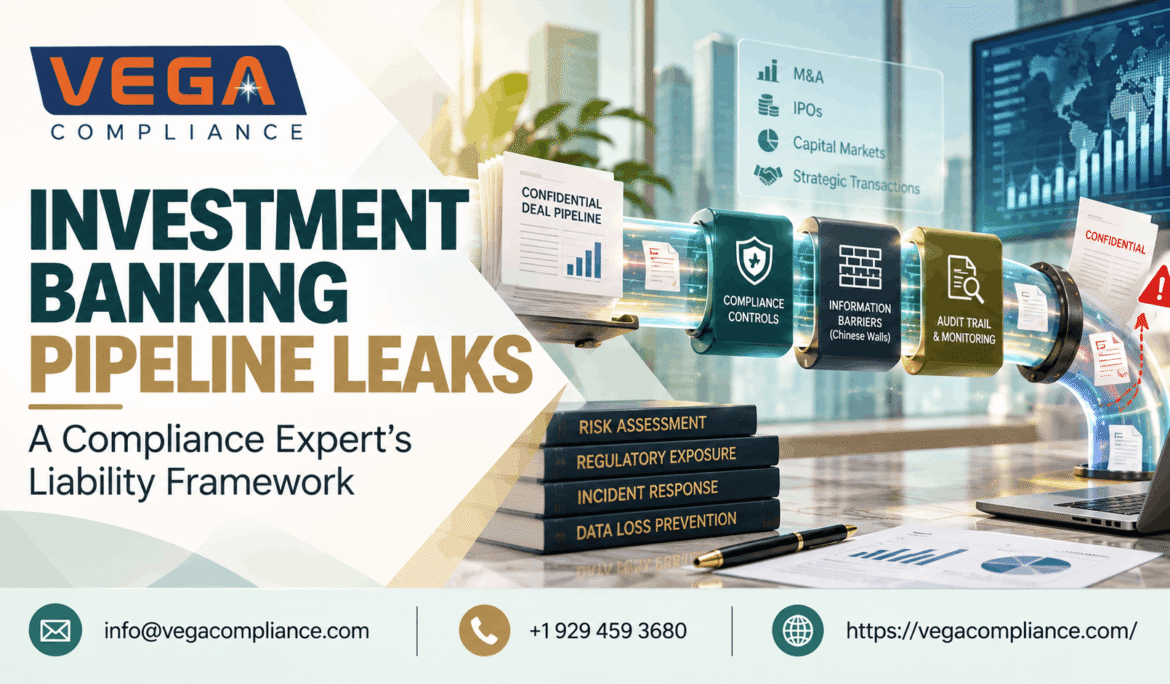
- Data Loss Prevention (DLP) Technology: Assessing whether automated DLP rules, attachment scanners, or email warning flags were active to identify sensitive internal deal code names or outbound attachments containing proprietary transaction rosters.
- Information Barriers (Chinese Walls): Examining whether access to internal deal pipelines was restricted on a strict “need-to-know” basis across investment banking divisions.
Auditing Mitigation and Response Protocols
Litigation outcomes frequently hinge on the promptness and efficacy of post-incident remediation:
- Immediate Response Protocols: Analyzing the speed and thoroughness of recall attempts, senior management escalation directives, and direct client communications.
- Corrective Actions: Evaluating post-leak operational adjustments, such as mandatory compliance training on email handling, to assess whether the firm effectively contained systemic exposure.
Assessing Causation and Financial/Market Harm
To support or rebut claims of actual damages, the expert coordinates with other experts to isolate breach-related impacts:
- Market Pricing & Liquidity Analysis: Determining whether disclosure of upcoming placements or block trades led to front-running, short selling, or depressed transaction valuations prior to launch.
- Client Relationship & Pipeline Churn: Distinguishing ordinary transaction cancellations or sponsor shifts from direct disengagements caused by the breach.
Key Analytical Assumptions
In conducting this liability review, a compliance expert explicitly identifies operational and evidentiary assumptions, including:
- Completeness of Audit Trails: Assuming production of raw email header logs, IT queue timestamps, and outbound email server configuration logs to verify transmission timelines and recall mechanics.
- Third-Party Handling: Assuming adherence to industry protocols by recipient counterparties (such as peer institutions instructing employees not to store or distribute misdirected materials).
- Public Availability Baseline: Assuming baseline market awareness of listed transactions prior to disclosure, differentiating widely known transactions from strictly confidential, non-public deals.
Conclusion & Legal Retainer Positioning
Inadvertent disclosures of high-value investment banking pipelines test the boundary between unavoidable human error and systemic control failure. In high-stakes litigation, court outcomes depend on precise, credible, and objective evaluations of financial institution standards of care, control efficacy, and regulatory compliance.
VEGA Compliance delivers expert witness testimony and regulatory consulting for defense and plaintiff counsel navigating complex financial market litigation. Our senior consultants combine decades of regulatory enforcement experience with deep technical expertise in information barriers, broker-dealer supervision, and financial data governance.
To discuss an active litigation matter or retain a compliance expert for liability analysis, contact our team at VEGA Compliance via www.vegacompliance.com.